
For that cause, practitioners often distinguish between design adequacy and operational effectiveness. For cybersecurity professionals responsible for protecting large and sophisticated organizations, security management validation is a mission-critical self-discipline that immediately impacts the enterprise’s risk posture and regulatory standing. Its operational, strategic, and governance implications are significant. The evolving regulatory panorama, with directives corresponding to DORA (Digital Operational Resilience Act), NIS2 (Network and Info Safety Directive), and the proposed UK Cyber Safety & Resilience Act, underscores this imperative. These laws are shifting the main target from static, audit-based compliance to a more demanding normal of demonstrable, ongoing operational resilience.
Validato: Empowering Your Journey To Integrated Security And Compliance
- We amplify human experience with AI insights to reduce the dangers that matter most to your corporation.
- Strengthen your ability to detect, reply to, and recuperate from cyberattacks through steady enchancment.
- Run ransomware, malware, and full kill-chain assaults towards EDR, XDR, EPP, and AV across Windows, Linux, and macOS to prove what they block and detect.
- Regardless of the precise technique you use, the secret’s finding an strategy to threat evaluation that works on your organization and being disciplined about performing it.
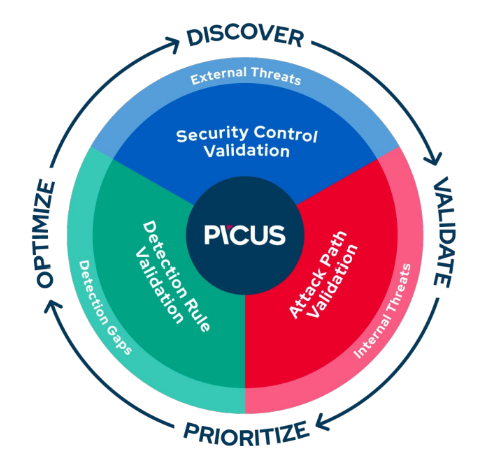
Conversely, a robust compliance framework offers the strategic course and impetus for more centered and effective validation efforts. Continuous security/control validation is a method of repeatedly testing security controls inside an organization to validate they work as intended, and then proactively handle any vulnerabilities. By rigorously testing and verifying digital property for exposed flaws, organizations can determine vulnerabilities, assess dangers, and make sure the effectiveness of their protective mechanisms. Let’s delve into the crucial elements of validation and its significance.
Active Directory Attack
In The End https://www.seomastering.com/audit/avvto.com/, these core ideas foster a safety tradition centered on measurable, repeatable, and evidence-based enchancment. For SOC managers, analysts, and safety architects, this is basic to maintaining resilience in a contemporary threat landscape. Configurations drift over time; validation catches when methods deviate from safe baselines.
It helps security groups determine policy weaknesses that would let attacks go unprevented and undetected. Controls drift as configurations change and as new threats appear daily, so validation ensures defenses stay optimized and that misconfigurations are caught earlier than a breach finds them first. In short, SCYTHE allows scalable, sensible, and effective steady safety controls validation — designed for the true world. In essence, security management validation operationalizes threat management for cybersecurity leaders, providing the evidence-based assurance wanted to take care of resilience, demonstrate due diligence, and justify ongoing security investments. Organizations could validate security controls quarterly or after major incidents, tool modifications, or architectural updates.
The Unbreakable Bond: How Security Controls Validation Fuels Continuous Compliance (and Vice-versa)
↻A swarm of AI brokers, Picus Swarm, runs this loop repeatedly and autonomously, so validation retains tempo as threats evolve and your surroundings modifications. Track management effectiveness as a development over time, so you’ll find a way to show progress, defend security spend, and hand leadership an audit-ready reply backed by evidence somewhat than assertion. Picus Breach and Attack Simulation, safely runs real-world attacks in opposition to your live defenses on a steady foundation, then shows you precisely what got through and the method to repair it.
Why Validate Your Controls?
It means guaranteeing that crucial safety controls usually are not solely designed and carried out correctly however are also persistently functioning successfully, adapting to new threats, and evolving with the business. Mechanically and repeatedly simulate real-world assaults towards your prevention and detection controls to see what they block, what they miss, and the way to fix the gaps. The SafeBreach breach and assault simulation (BAS) platform puts your defenses toe-to-toe in opposition to over 30,000 assault strategies to supply unparalleled visibility into your security posture. See why a few of the largest enterprises in the world belief SafeBreach to help them proactively establish and remediate vulnerabilities. Security teams personal and function dozens of instruments, but misconfigurations or drift over time can mean those instruments aren’t successfully defending towards assaults.